Hi all,
Today I came up with a situation to create email address in AWS and landed in AWS Workmail.
Prerequisites: Domain Registrar login details for updating the NS or Dns records. If your registrar is not providing dns management then use the AWS Route53 service for managing the dns records.
In this service we need to setup this as below:
1) Create an Organization. The Web application url will have a tail end like .awsapps.com/mail . If your organization is abc then the workmail web application url will be like https://abc.awsapps.com/mail

2) After creating the organization you need to click on it and now create the Domain for email address.

3) Once you create the domain , it should be verified by adding the TXT dns records and the remaining MX, CNAME and SPF records in the dns management (Route53)
> Verify domain ownership (required)
> Finalize mail setup (required)
> Increase security (recommended)
 It will take 5 to 10 Minutes for the dns entries to be get verified. So after adding the entries please wait for some time before clicking on the refresh button.
4) Once the domain is verified you can create the user, which is email addresses.

5) Finally configure the email id in your thunderbird.

 6) Please see the dns entries as below:

In thunderbird select SSL/TLS with Normal Password. That is all. Happy mailing.
Today I came up with a situation to create email address in AWS and landed in AWS Workmail.
Prerequisites: Domain Registrar login details for updating the NS or Dns records. If your registrar is not providing dns management then use the AWS Route53 service for managing the dns records.
In this service we need to setup this as below:
1) Create an Organization. The Web application url will have a tail end like .awsapps.com/mail . If your organization is abc then the workmail web application url will be like https://abc.awsapps.com/mail

2) After creating the organization you need to click on it and now create the Domain for email address.

3) Once you create the domain , it should be verified by adding the TXT dns records and the remaining MX, CNAME and SPF records in the dns management (Route53)
> Verify domain ownership (required)
> Finalize mail setup (required)
> Increase security (recommended)

4) Once the domain is verified you can create the user, which is email addresses.

5) Finally configure the email id in your thunderbird.
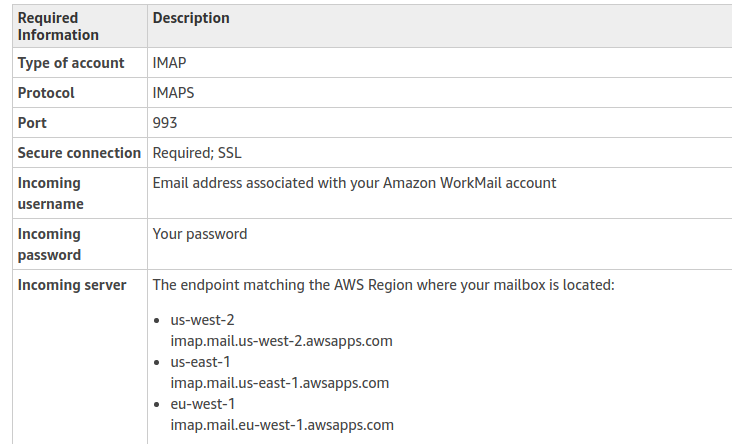


In thunderbird select SSL/TLS with Normal Password. That is all. Happy mailing.
Comments